Pass-Sure CS0-003 Valid Test Online–Pass CS0-003 First Attempt
This version is designed especially for those CS0-003 test takers who cannot go through extensive CompTIA CS0-003 practice sessions due to a shortage of time. Since the CompTIA CS0-003 PDF file works on smartphones, laptops, and tablets, one can use CompTIA CS0-003 dumps without limitations of place and time. Additionally, these CompTIA CS0-003 PDF questions are printable as well.
CompTIA Cybersecurity Analyst (CySA+) Certification is an intermediate-level certification that is designed for IT professionals who are involved in the cybersecurity field. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification exam covers a wide range of cybersecurity topics, including threat management, vulnerability management, incident response, and compliance and assessment. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is recognized by employers worldwide and is in high demand. It is an ideal certification for professionals who are looking to advance their careers in cybersecurity and want to demonstrate their skills and knowledge in this field.
>> CS0-003 Valid Test Online <<
CS0-003 Valid Test Online - Pass Guaranteed Quiz 2025 CS0-003: CompTIA Cybersecurity Analyst (CySA+) Certification Exam First-grade Latest Mock Exam
In order to better meet users' need, our CompTIA Cybersecurity Analyst (CySA+) Certification Exam study questions have set up a complete set of service system, so that users can enjoy our professional one-stop service. We not only in the pre-sale for users provide free demo, when buy the user can choose in we provide in the three versions, at the same time, our CS0-003 training materials also provides 24-hour after-sales service, even if you are failing the exam, don't pass the exam, the user may also demand a full refund with purchase vouchers, make the best use of the test data, not for the user to increase the economic burden. Such a perfect one-stop service of our CS0-003 Test Guide, believe you will not regret your choice, and can better use your time, full study, efficient pass the exam.
CompTIA Cybersecurity Analyst (CySA+) Certification Exam Sample Questions (Q16-Q21):
NEW QUESTION # 16
The Chief Information Security Officer wants to eliminate and reduce shadow IT in the enterprise. Several high-risk cloud applications are used that increase the risk to the organization. Which of the following solutions will assist in reducing the risk?
- A. Configure MFA with strict access
- B. Deploy a CASB and enable policy enforcement
- C. Enable SSO to the cloud applications
- D. Deploy an API gateway
Answer: B
Explanation:
A cloud access security broker (CASB) is a tool that can help reduce the risk of shadow IT in the enterprise by providing visibility and control over cloud applications and services. A CASB can enable policy enforcement by blocking unauthorized or risky cloud applications, enforcing data loss prevention rules, encrypting sensitive data, and detecting anomalous user behavior.
NEW QUESTION # 17
A company has the following security requirements:
. No public IPs
All data secured at rest
. No insecure ports/protocols
After a cloud scan is completed, a security analyst receives reports that several misconfigurations are putting the company at risk. Given the following cloud scanner output:
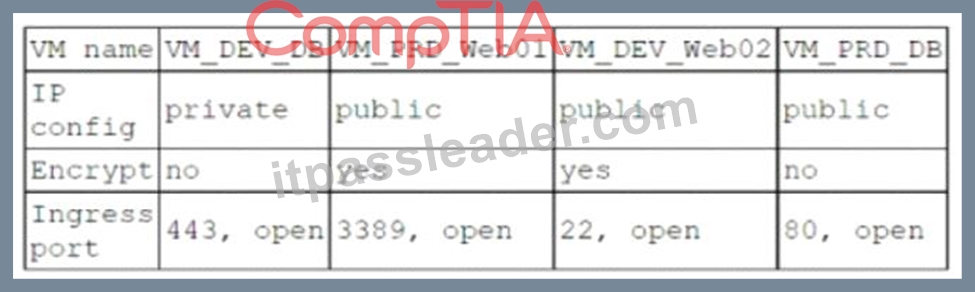
Which of the following should the analyst recommend be updated first to meet the security requirements and reduce risks?
- A. VM_PRD_Web01
- B. VM_DEV_Web02
- C. VM_DEV_DB
- D. VM_PRD_DB
Answer: A
Explanation:
This VM has a public IP and an open port 80, which violates the company's security requirements of no public IPs and no insecure ports/protocols. It also exposes the VM to potential attacks from the internet. This VM should be updated first to use a private IP and close the port 80, or use a secure protocol such as HTTPS.
References[CompTIA CySA+ Study Guide: Exam CS0-003, 3rd Edition], Chapter 2: Cloud and Hybrid Environments, page 67.[What is a Public IP Address?][What is Port 80?]
NEW QUESTION # 18
A security analyst receives an alert for suspicious activity on a company laptop An excerpt of the log is shown below:
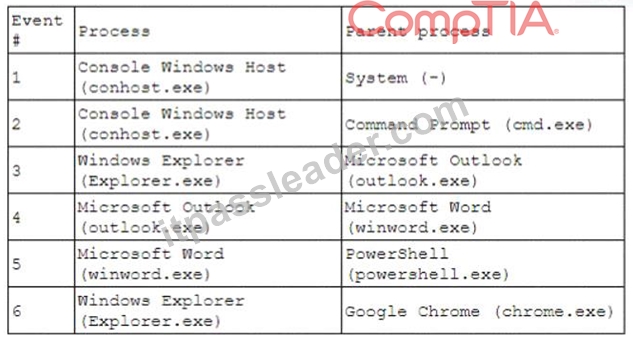
Which of the following has most likely occurred?
- A. A web browser vulnerability was exploited.
- B. A credential-stealing website was visited.
- C. An Office document with a malicious macro was opened.
- D. A phishing link in an email was clicked
Answer: C
Explanation:
An Office document with a malicious macro was opened is the most likely explanation for the suspicious activity on the company laptop, as it reflects the common technique of using macros to execute PowerShell commands that download and run malware. A macro is a piece of code that can automate tasks or perform actions in an Office document, such as a Word file or an Excel spreadsheet. Macros can be useful and legitimate, but they can also be abused by threat actors to deliver malware or perform malicious actions on the system. A malicious macro can be embedded in an Office document that is sent as an attachment in a phishing email or hosted on a compromised website. When the user opens the document, they may be prompted to enable macros or content, which will trigger the execution of the malicious code. The malicious macro can then use PowerShell, which is a scripting language and command-line shell that is built into Windows, to perform various tasks, such as downloading and running malware from a remote URL, bypassing security controls, or establishing persistence on the system. The log excerpt shows that PowerShell was used to download a string from a URL using the WebClient.DownloadString method, which is a common way to fetch and execute malicious code from the internet. The log also shows that PowerShell was used to invoke an expression (iex) that contains obfuscated code, which is another common way to evade detection and analysis.
The other options are not as likely as an Office document with a malicious macro was opened, as they do not match the evidence in the log excerpt. A credential-stealing website was visited is possible, but it does not explain why PowerShell was used to download and execute code from a URL. A phishing link in an email was clicked is also possible, but it does not explain what happened after the link was clicked or how PowerShell was involved. A web browser vulnerability was exploited is unlikely, as it does not explain why PowerShell was used to download and execute code from a URL.
NEW QUESTION # 19
The Chief Information Security Officer is directing a new program to reduce attack surface risks and threats as part of a zero trust approach. The IT security team is required to come up with priorities for the program. Which of the following is the best priority based on common attack frameworks?
- A. Employ a network-based IDS
- B. Enable SSO to enterprise applications
- C. Conduct thorough incident response
- D. Reduce the administrator and privileged access accounts
Answer: D
Explanation:
The best priority based on common attack frameworks for a new program to reduce attack surface risks and threats as part of a zero trust approach is to reduce the administrator and privileged access accounts. Administrator and privileged access accounts are accounts that have elevated permissions or capabilities to perform sensitive or critical tasks on systems or networks, such as installing software, changing configurations, accessing data, or granting access.
Reducing the administrator and privileged access accounts can help minimize the attack surface, as it can limit the number of potential targets or entry points for attackers, as well as reduce the impact or damage of an attack if an account is compromised.
NEW QUESTION # 20
A security analyst is reviewing events that occurred during a possible compromise. The analyst obtains the following log:
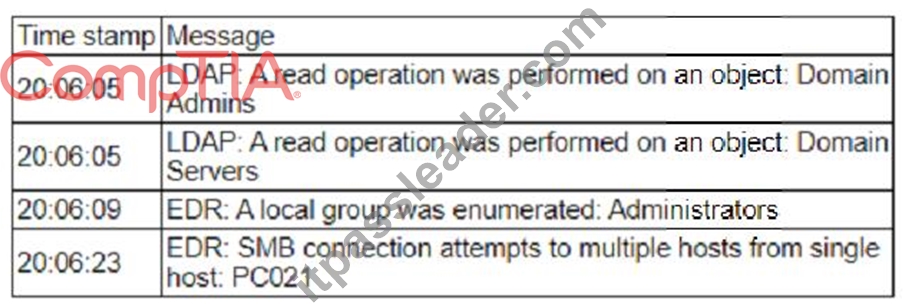
Which of the following is most likely occurring, based on the events in the log?
- A. An adversary is escalating privileges.
- B. An adversary is performing a vulnerability scan.
- C. An adversary is attempting to find the shortest path of compromise.
- D. An adversary is performing a password stuffing attack.
Answer: B
Explanation:
.
Explanation:
Based on the events in the log, the most likely occurrence is that an adversary is performing a vulnerability scan. The log shows LDAP read operations and EDR enumerating local groups, which are indicative of an adversary scanning the system to find vulnerabilities or sensitive information. The final entry shows SMB connection attempts to multiple hosts from a single host, which could be a sign of network discovery or lateral movement. Reference: CompTIA CySA+ Study Guide: Exam CS0-003, 3rd Edition, Chapter 4: Security Operations and Monitoring, page 161; Monitor logs from vulnerability scanners, Section: Reports on Nessus vulnerability data.
NEW QUESTION # 21
......
We promise you that if you fail to pass your exam after using CS0-003 exam materials, we will give you refund. We are pass guarantee and money back guarantee. Moreover, CS0-003 training materials cover most of knowledge points for the exam, and you can master the major knowledge points as well as improve your professional ability after practicing. CS0-003 Exam Materials contain both questions and answers, and it’s convenient for you to have a quickly check after practicing. We also have online and offline chat service, if you have any questions about CS0-003 exam dumps, you can consult us.
Latest CS0-003 Mock Exam: https://www.itpassleader.com/CompTIA/CS0-003-dumps-pass-exam.html


